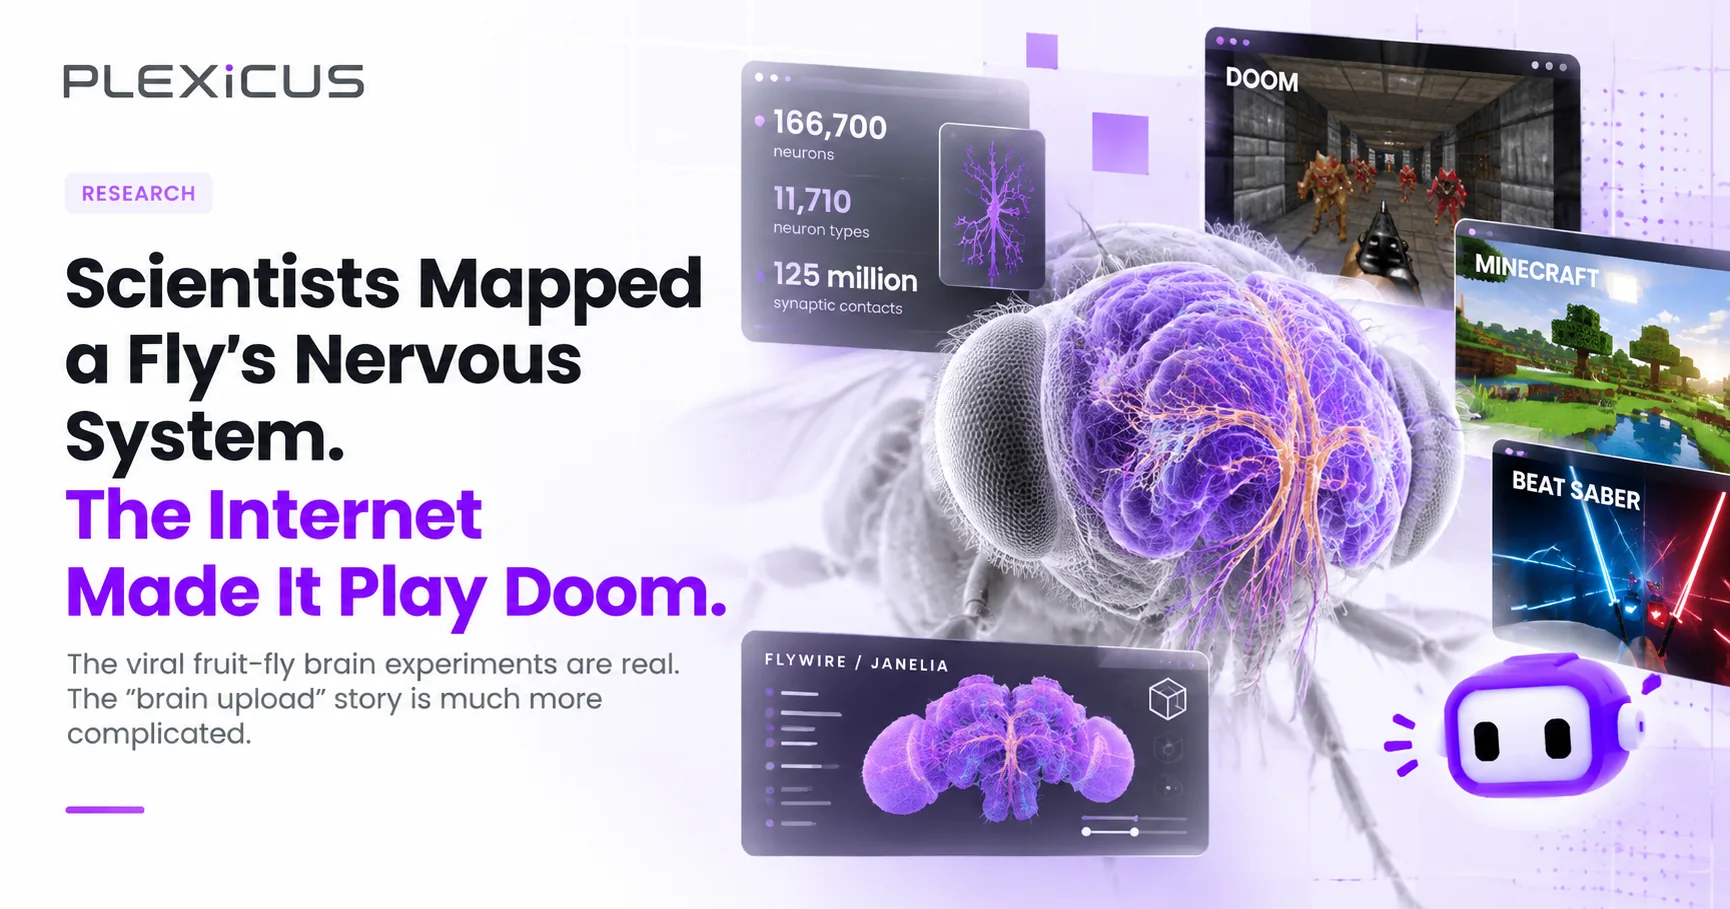
Scientists Mapped a Fly’s Nervous System. The Internet Made It Play Doom
The fly connectome became a gaming meme. Its most revealing experiments ask a harder question: what does the biological wiring actually contribute?
José Ramón Palanco is the CEO/CTO of Plexicus, a pioneering company in ASPM (Application Security Posture Management) launched in 2024, offering AI-powered remediation capabilities. Previously, he founded Dinoflux in 2014, a Threat Intelligence startup that was acquired by Telefonica, and has been working with 11paths since 2018. His experience includes roles at Ericsson`s R&D department and Optenet (Allot). He holds a Telecommunications Engineering degree from the University of Alcala de Henares and a Master`s in IT Governance from the University of Deusto. As a recognized cybersecurity expert, he has been a speaker at various prestigious conferences including OWASP, ROOTEDCON, ROOTCON, MALCON, and FAQin. His contributions to the cybersecurity field include multiple CVE publications and the development of various open source tools such as nmap-scada, ProtocolDetector, escan, pma, EKanalyzer, SCADA IDS, and more.
The fly connectome became a gaming meme. Its most revealing experiments ask a harder question: what does the biological wiring actually contribute?
DevDay 2026 connected persistent agents, cloud coding, plugins, events, and shared work. Here is what shipped, what is still coming, and where AppSec boundaries lie.
Opus 5.5 motion-graphics demos reveal an agentic loop: plan, write code, run it, inspect, revise. Claude cybersecurity now depends on verification keeping pace.
Jev AI returns typed decisions instead of prose. That could change where semantic judgment fits in security workflows, if teams keep policy, fallbacks, verification, and human review.
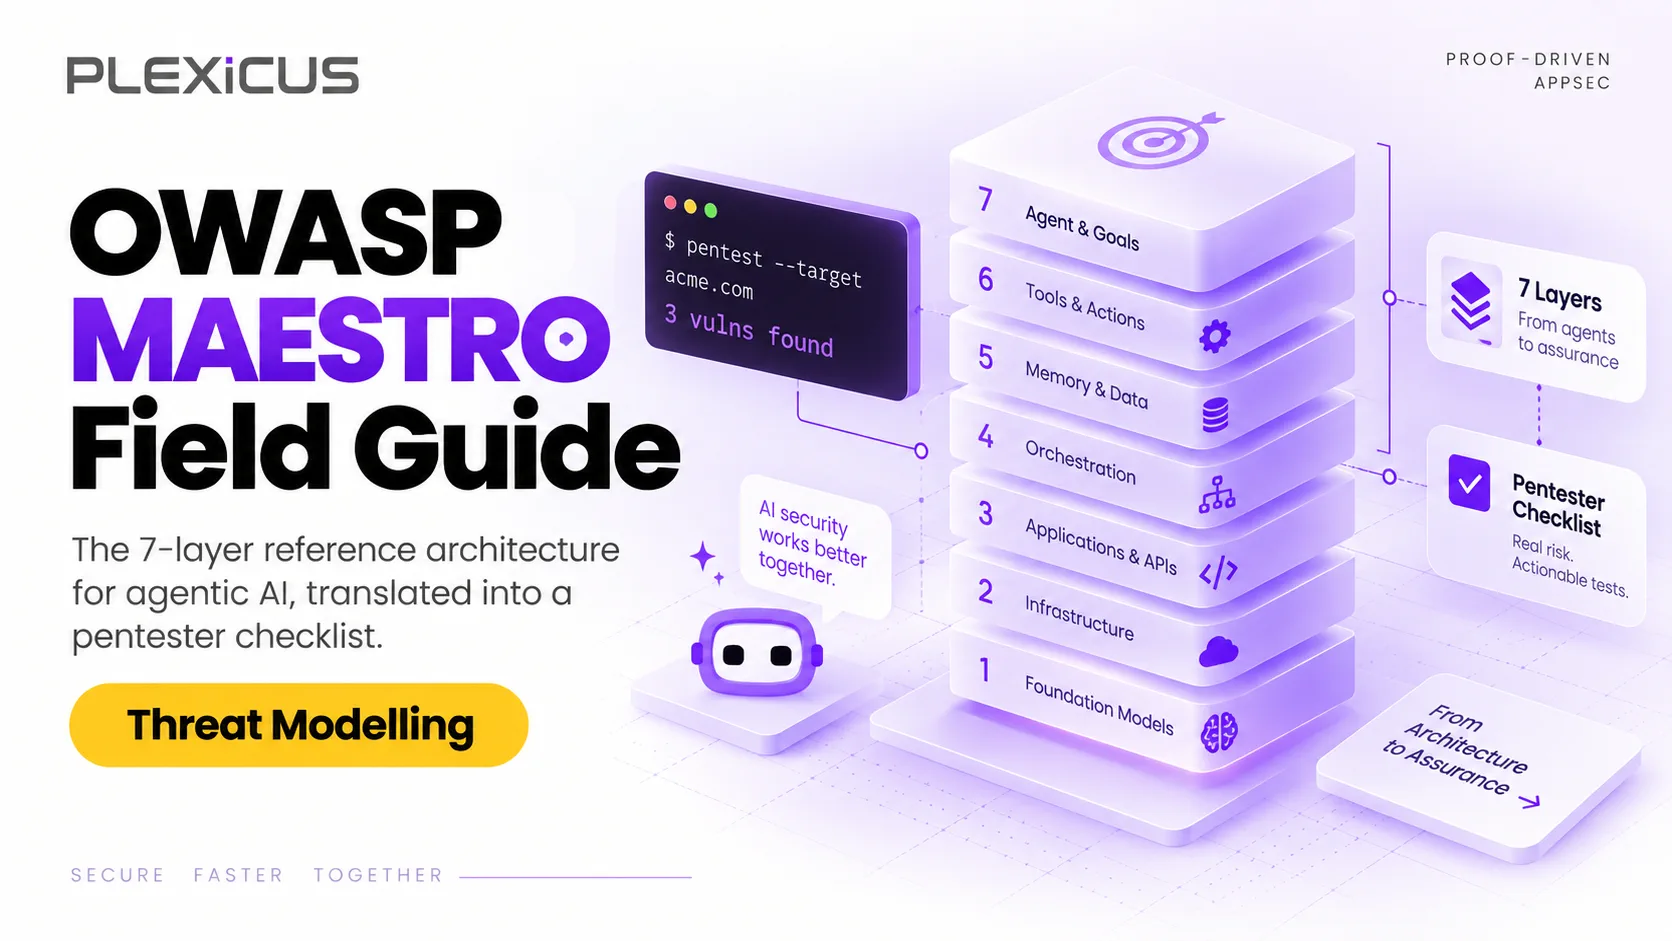
MAESTRO is the Cloud Security Alliance's 7-layer framework for agentic AI threat modeling, applied by the OWASP GenAI Security Project. This guide turns each layer into a pentest checklist.
AI penetration testing in 2026 splits into three lanes: autonomous pentest agents, BAS platforms and AI-assisted PTaaS. We compared 15 tools on signed-scope evidence, replay and pricing.
Proof-Driven AppSec is a vulnerability remediation process that closes the loop from alert to merged fix once, with replayable evidence at every step: detect, verify, fix, audit.
AI can remove repetitive AppSec work without removing accountability. Learn how to decide what to automate, what to augment, and when a security decision should be escalated to a person.
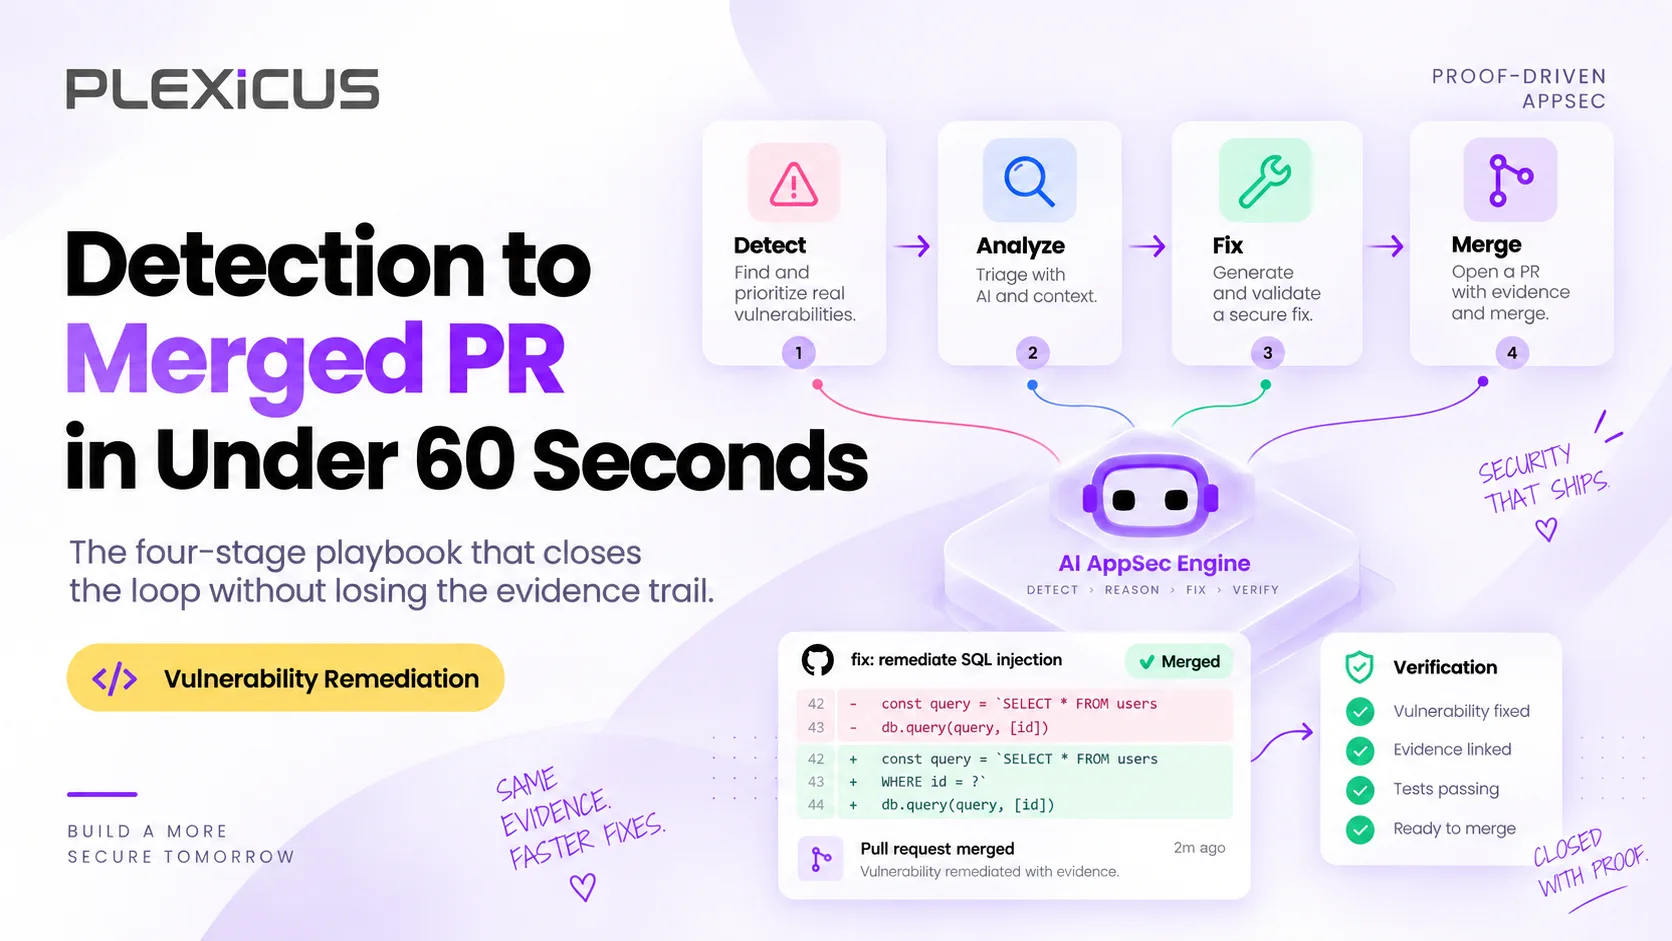
A four-step automated vulnerability remediation playbook that turns a verified finding into a tested, reviewer-ready PR in under 60 seconds, with the evidence attached.
Running `trivy image` isn't DevSecOps—it's noise generation. Real security engineering is about signal-to-noise ratio. This guide provides production-grade configurations for 17 industry-standard tools to stop vulnerabilities without stopping the business, organized into three phases: pre-commit, CI gatekeepers, and runtime scanning.
Installing a security tool is the easy part. The hard part begins on 'Day 2,' when that tool reports 5,000 new vulnerabilities. This guide focuses on vulnerability management: how to filter out duplicate alerts, manage false positives, and track the metrics that actually measure success. Learn how to move from 'finding bugs' to 'fixing risks' without overwhelming your team.
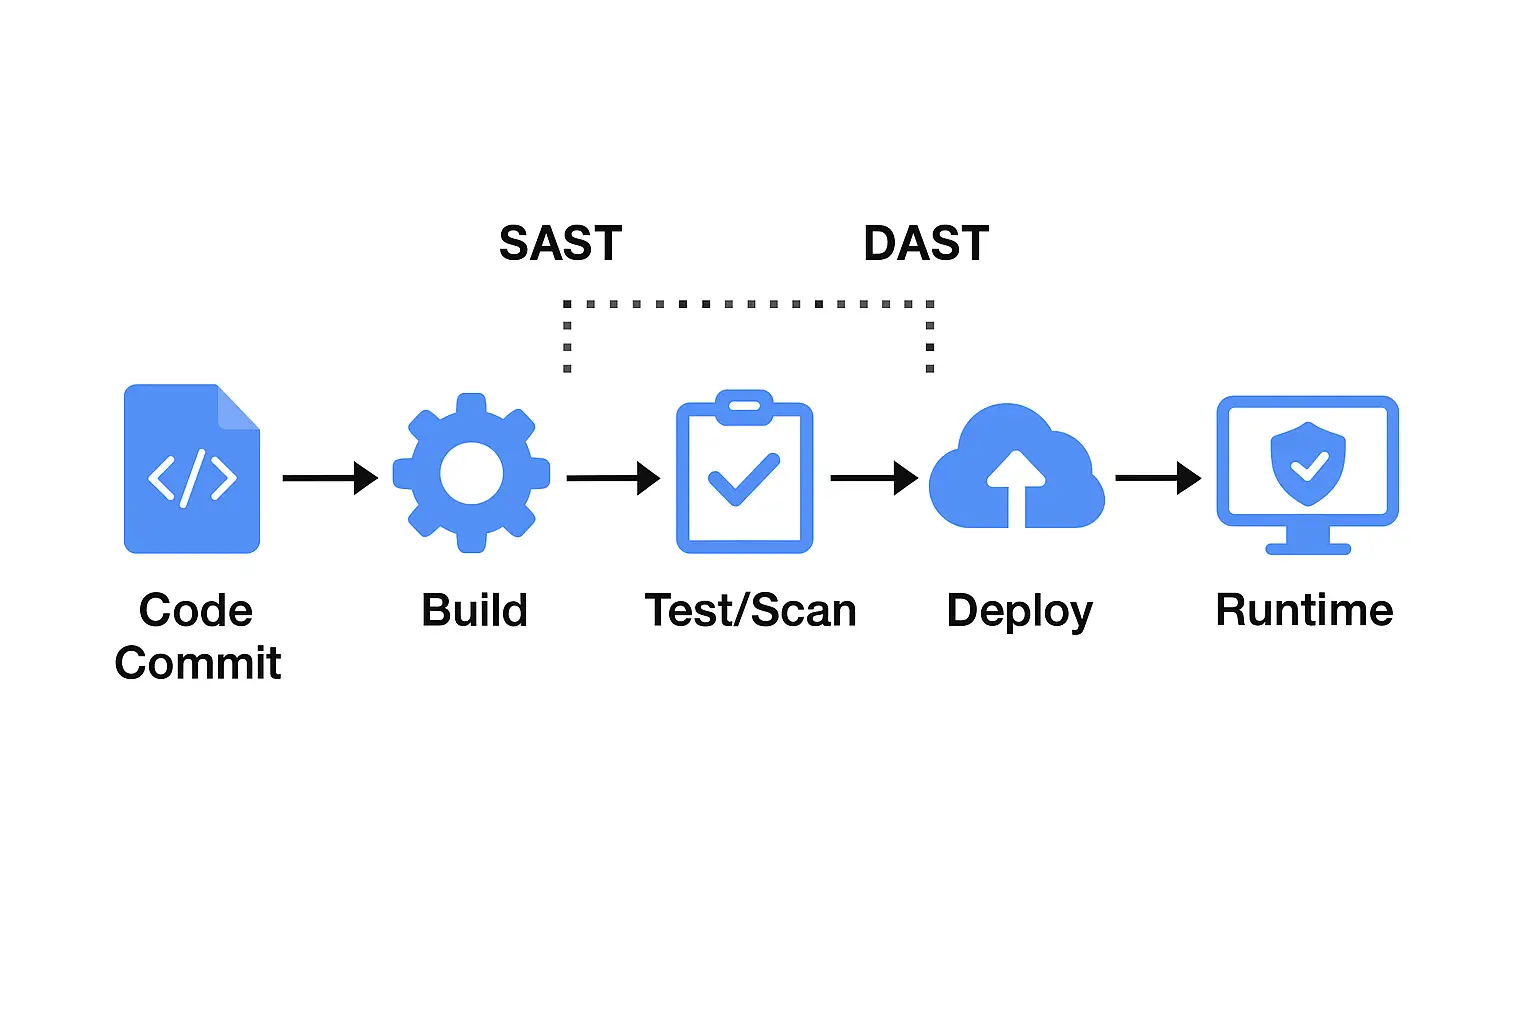
SAST and DAST are security testing methods used to protect applications from attacks. To see how each one helps with application security, let’s look at their differences and where they fit in your workflow
Compare leading ASPM tools like Plexicus, Cycode, Wiz, and Apiiro to automate AppSec testing and vulnerability management
Discover top API security tools to detect vulnerabilities, stop API attacks, and protect your applications with advanced scanning and testing.
Modern applications depend a lot on third-party and open-source libraries. This speeds up development, but it also increases the risk of attacks. Each dependency can introduce issues like unpatched security flaws, risky licenses, or outdated packages. Software Composition Analysis (SCA) tools help address these problems.
There are dozens of SAST tools on the market, ranging from open-source to enterprise-grade. The challenge is: Which SAST tool is best for your team?
Web application security is essential to protect your apps from cyberattacks that target sensitive data and disrupt operations. This guide covers the importance of web app security, common vulnerabilities, best practices, and testing methods, helping you secure your application, ensure compliance, and maintain user trust
A nightmare security breach has become a reality for many European companies. Learn the 15 transformative DevSecOps trends you must know to stay off the breach list.
Plexicus graduates from Startup Wise Guys Spring Batch 2025 accelerator program.
If you’re building or running software today, you’re probably juggling micro-services, serverless functions, containers, third-party packages, and an avalanche of compliance check-boxes. Each moving part spawns its own findings, dashboards, and angry red alerts. Before long, risk visibility feels like driving in San Francisco fog at 2 a.m.—you know danger’s out there, but you can’t quite see it.
Plexicus has secured a $150,000 investment from Microsoft to expand its cloud infrastructure. This funding will enhance system performance, scalability, and reliability, enabling Plexicus to support more businesses with AI-powered enterprise solutions.
Discover how Plexicus' new BlackDuck integration enhances open-source security with real-time vulnerability detection, automated risk prioritization, and seamless DevSecOps workflows.
Plexicus launches AI-driven security platform for real-time vulnerability remediation. Autonomous agents detect, prioritize, and fix threats instantly.
A new collaboration between Plexicus and Céfiros is set to enhance application security across 19 countries in Latam and Iberia. This cybersecurity collaboration brings advanced Application Security Posture Management (ASPM) solutions to organizations seeking to proactively defend against cyber threats.

Frameworks like DORA, ISO 27001, and NIST SP 800-53 is essential for robust Application Security Posture Management, helping organizations meet standards, reduce risks, and maintain regulatory compliance.
Plexicus is Proof-Driven AppSec: validated findings, contextual understanding, and reviewed remediation — anchored in evidence, scoped with you.