REMEDIATION

Detecting is not fixing.

Once a finding is verified, Plexicus prepares the remediation context and a suggested change for your team. Your team keeps merge control — Plexicus never pushes to production.

Product views use synthetic demo data. No customer data is shown.
THE PIPELINE

From a verified finding to a reviewed change — without losing the thread.

Every step keeps the original evidence attached. Reviewers see the same context the engineers do.

01

Verified finding

Only findings that your team has reviewed reach the remediation step. The rest are kept aside with their context intact.

02

Context preserved

Affected flow, reach, weakness class, and rationale are bundled into the proposed change — so the reviewer sees the full picture.

03

Suggested change

A reviewer-ready diff is prepared with the original finding explained inline. Regression tests and notes are included where relevant.

04

Reviewer-ready handover

The change lands in your existing repo with reviewer assignment and a re-test hook wired to CI. Your team merges or rejects with evidence.

PRODUCT VIEW

See the remediation workflow in context.

Plexicus Remediation workflow, shown with synthetic demo data.
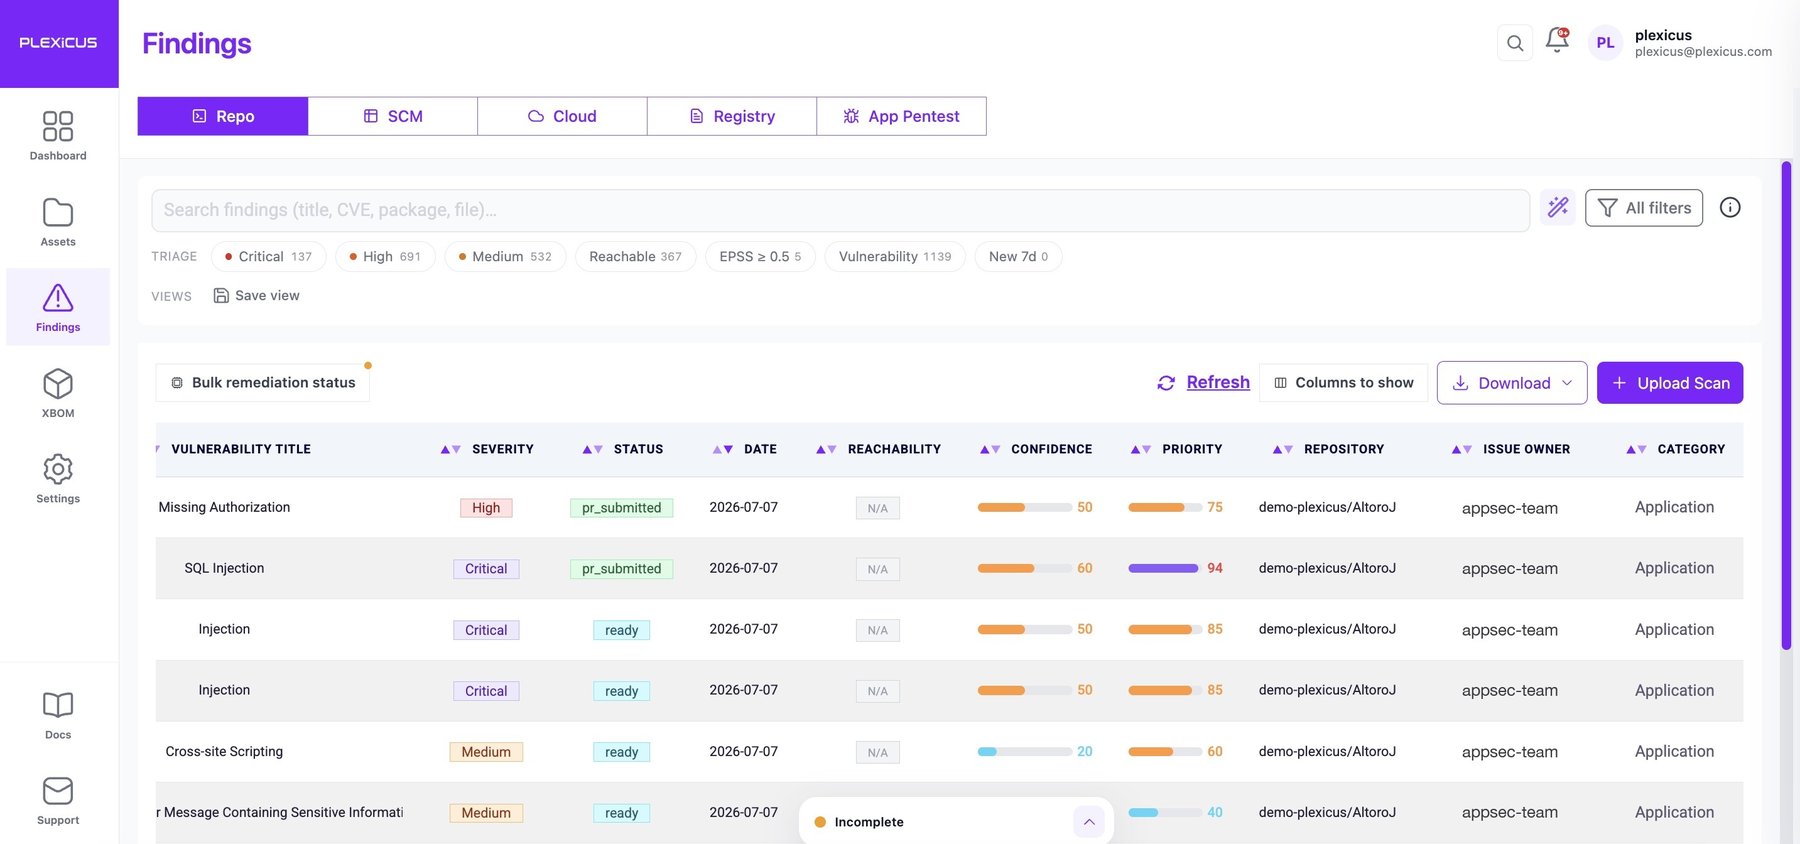
Plexicus product view showing security context and reviewed evidence
STEP 1 Security context
Plexicus findings view showing severity and review context
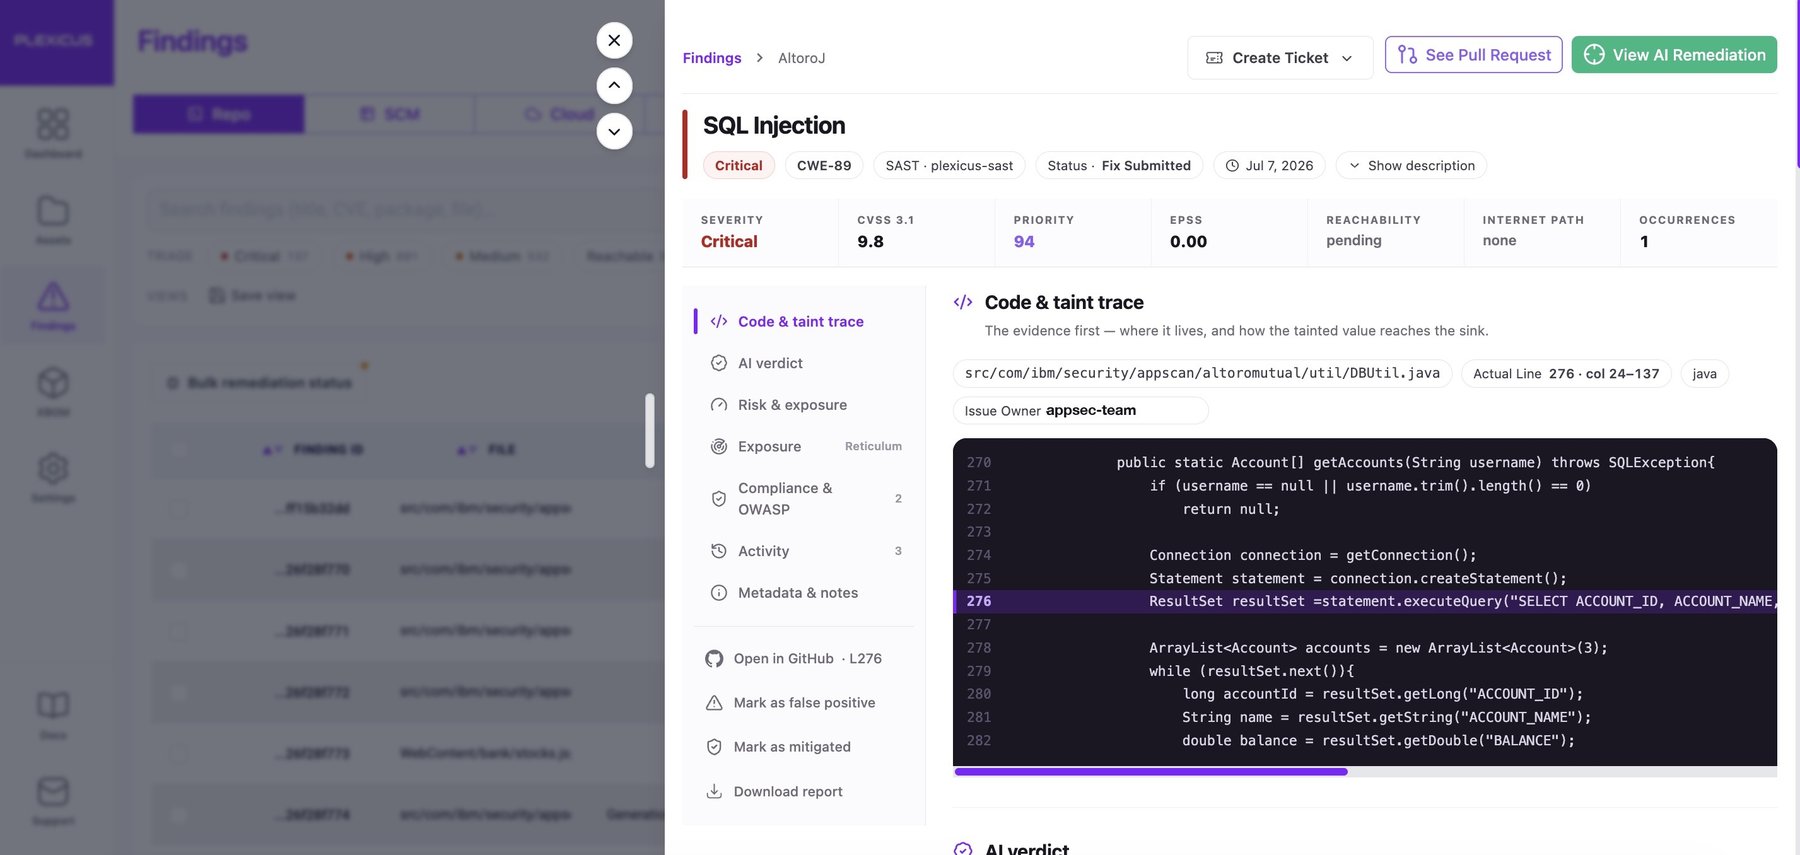
STEP 2 Validated finding context
Plexicus finding detail showing a remediation proposal for review
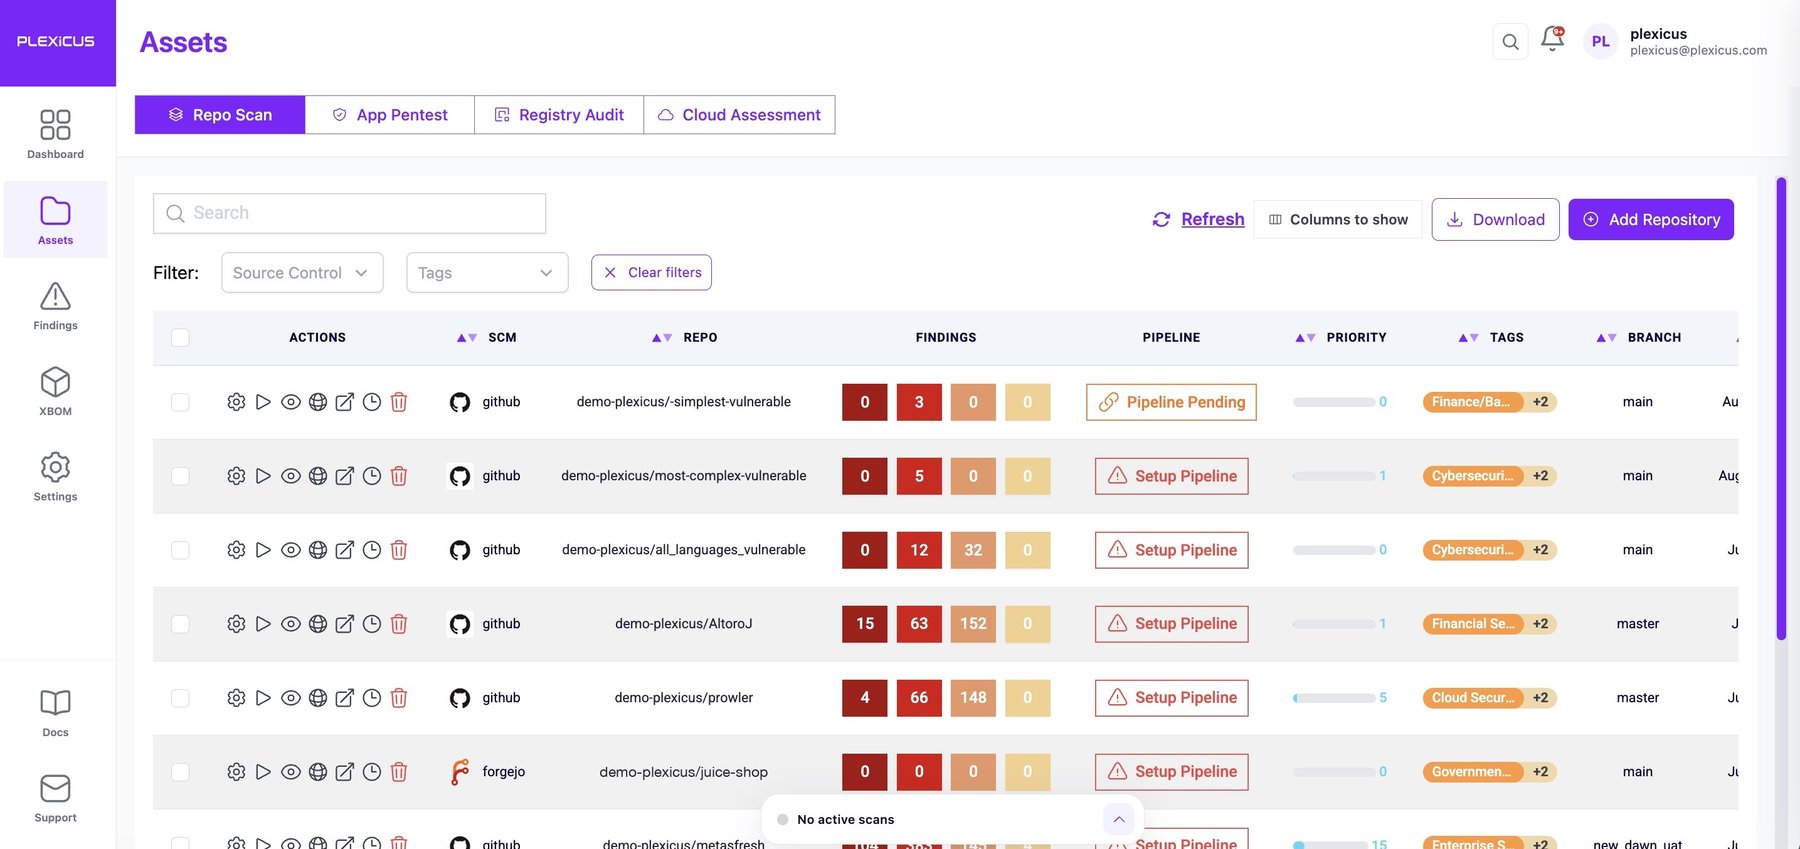
STEP 3 Reviewer-ready change

Product views use synthetic demo data. No customer data is shown.

WHAT GETS REVIEWED

Reviewable patches built for AI-generated code.

Plexicus does not paper over a finding — the proposed change removes the class of vulnerability that produced it.

FIX 01

AI-introduced flaws

Phantom packages, prompt-injection sinks, authz gaps, hallucinated secrets. The patterns LLM assistants introduce — addressed at the source.

FIX 02

Classic SAST findings

SQL injection, XSS, SSRF, insecure deserialization, weak crypto. Plexicus prepares reviewed patches for the OWASP Top 10 with regression tests attached.

FIX 03

Business-logic flaws

Broken object-level authorization, missing rate limits, privilege escalation. The flaws SAST misses — surfaced via reachability, addressed via review.

FIX 04

Supply-chain exposure

Typosquatted and slopsquatted dependencies replaced with the canonical upstream — including version pinning and lockfile updates.

THE PROOF

Every suggested change ships with the evidence that produced it.

Reviewed by Your team · context attached for the reviewer
Capability class Bound to the canonical advisory database (CWE)
Fix explanation Rationale, regression tests, and impact summary attached to the proposed change.
Lines changed Suggested diff scope · ready for your reviewer
Re-test Re-test hook wired to CI · your team verifies before merge.
THE PROCESS

Reviewable patches prepared for your team.

Plexicus prepares the work — your team owns the merge.

1

reviewable change prepared per verified finding

100%

of suggested changes ship with evidence attached

0

changes pushed to production without reviewer approval

WORKFLOW

Plays nicely with the tools your team already uses.

Suggested changes land where your engineers work. Findings sync to your tracker. Audit evidence flows to your GRC. Plexicus never sits between a developer and their repo.

Repositories GitHub · GitLab · Bitbucket
Tracker Linear · GitHub Issues
Chat Slack · Microsoft Teams
Alerting PagerDuty · Opsgenie
GRC Drata · Vanta · Tugboat Logic
REMEDIATION

See a reviewed change land in your repo.

Book a 30-minute walkthrough. We'll walk through a verified finding end-to-end against a sample repo and show the proposed change your team reviews.

Qualification

Check whether AI Swarm Pentest fits your environment.

Share the minimum context. We will review the scope and tell you the next commercial step.

Before submitting — verify you fit

0 / 280

No commitment. If you don't fit, we'll tell you.

SAMPLE HANDOVER · ILLUSTRATIVE

Sample evidence handover

A trimmed view of what your team receives at the end of an AI Swarm Pentest engagement. Real engagements include full technical evidence, executive narrative, and a remediation plan.

VALIDATED FINDING Evidence attached

Server-Side Request Forgery in webhooks/receiver

demo-project/sample-app · src/webhooks/receiver.py:42

SeverityHigh CVSS 3.18.6 Priority79 Confirmedvia replay

Untrusted caller-supplied URLs reach an internal egress without an allowlist. Replayed in a sandbox against a fresh authorized target — the same control was validated to fail twice.

REVIEWER-READY REMEDIATION Merge-ready PR

Validate the target URL against an allowlist of permitted hostnames. Reject private/internal IP ranges. Enforce HTTPS only.

plexicus/remediation/webhooks-ssrf 3 changed · 0 new files
42resp = requests.get(target_url)
42+if not is_allowed_host(target_url):
43+  raise WebhookRejected(target_url)
44+resp = requests.get(target_url, timeout=5)
Every engagement hands over:
  • Executive briefing
  • Validated findings list
  • Merge-ready PRs
  • Compliance mapping (NIS2 · DORA · CRA)
Private Round For investors